Cyber News / Article / Palo Alto Networks Named a Leader in the 2026 Gartner® Magic Quadrant™ for Privileged Access Management
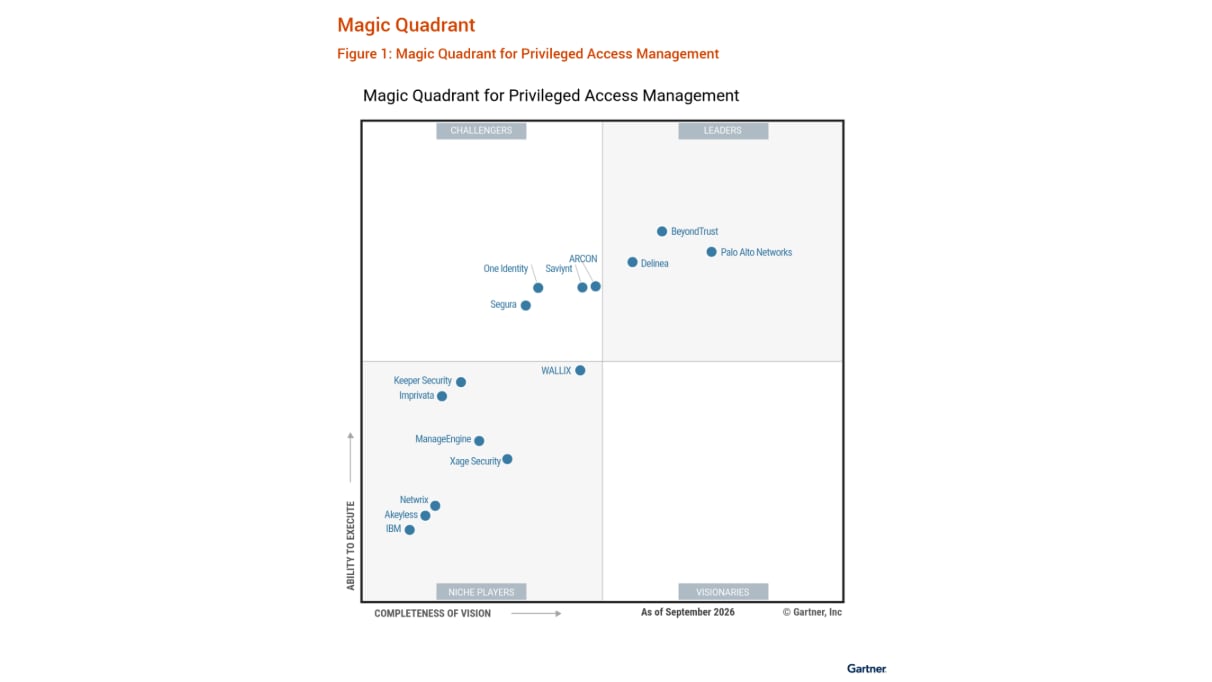
Palo Alto Networks Named a Leader in the 2026 Gartner® Magic Quadrant™ for Privileged Access Management
For the eighth consecutive time,Palo Alto Networksis recognized as a Leader in the 2026 Gartner®Magic Quadrant™ for Privileged AccessManagement.Once again, it is positioned furthest along in Completeness of Vision and has been positioned so in every Magic Quadrant published for this category.
Read the 2026 Gartner®Magic Quadrant™ for Privileged Access Management.
Identity is not a siloed risk. As an increasingly attractive target for threat actors, it must be understood and secured across the entire attack surface.For our customers, the benefit is clear: as part of Palo Alto Networks, Idira helps you adopt AI innovation at speed while retaining control over privileged access.
The 2026 Gartner Magic Quadrant evaluates providers across their Ability to Execute and Completeness of Vision. We feel that being positioned furthest in Completeness of Vision matters most in moments of technology change like this one. Idira is built for an environment where:
Customers need a partner that can execute on an innovative vision as the threat and technology landscape evolves. With the scale of Palo Alto Networks behind us, we are focused on securing every identity and every moment of privilege in the AI enterprise.
We are in a new era, where identity and access have fundamentally changed. Machine identities nowoutnumber humans 109 to 1, AI agents (which require access to enterprise systems to do useful work) are entering the workforce, andattackers have noticed. That access must be governed alongside the human and machine identities already protected. Increasingly, though, attackers log in rather than break in, andPAMmust evolve to stay ahead of these challenges. PAM must now extend beyond vaulted administrator credentials to discover, control, and govern privilege across the enterprise.
Idira’s Modern PAM platform is enabling PAM to meet the demands of the AI era; it combines vaulted access andzero standing privileges(ZSP) with secrets management,workload security, andidentity governance. We are bringing ZSP to every modern target, including cloud, apps, andKubernetes. And access challenges go beyond humans, so Idira does as well. To secure non-human access, Idira addednative SPIFFE/SVIDsupport to deliver short-lived cryptographic identities to workloads and AI agents. Our ability to deliver and innovate on our vision enables Idira to deliver purpose-built, end-to-end protection at scale for the modern AI enterprise.
Making modern PAM easier to adopt is central to our approach.
While some of the largest organizations continue to trust Idira for our proven traditional PAM leadership, they now also rely on us to guide their modern PAM transformation initiatives.
Data-Driven Innovation: We believe that our Transformation Decision Engine, which uses customer environment data to quantify the value of PAM modernization, combined with our years of proven experience guiding both the implementation and modernization of PAM programs across our expansive customer base, demonstrates our ability to help customers through any stage of their PAM journey with an informed, data-driven approach.
Customer Experience:Idira guides cross-functional security teams through complex operational shifts, from standing access to ZSP, supported by theIdira Blueprint, hands-on training, and an active peer community.
Scale and Reach:Idira customers already have a partner with global reach, and joining Palo Alto Networks extends it further. Our security platform sees identity risk across the whole attack surface, so a stolen or abused privilege becomes a signal your defenses act on in the moment, backed by the investment and expertise of the industry's largest cybersecurity company.
Eight reports, eight times furthest in vision. I'm grateful to the customers whose trust and expertise shaped every one of them. This is also a first, as it’s the first report to carry the Palo Alto Networks name. Since Idira joined forces with Palo Alto Networks, ourPAM expertiseand platform now sit inside the industry's leading cybersecurity company, where privileged access connects toreal-time threat detection and response,AI security, andUnit 42 threat intelligence.
The next chapter of privileged access is being written now, by attackers with frontier AI models and by enterprises deciding how fast to move. We intend to stay furthest ahead of both.
Thank you to our customers and community for your trust, and for the partnership that helps shape our innovation.
Gartner, Magic Quadrant for Privileged Access Management, Paul Mezzera, Shubham Gera, Tarun Rohilla, Scott Brinker, 21 October 2026.
Gartner and Magic Quadrant are trademarks of Gartner, Inc. and/or its affiliates.
Gartner does not endorse any company, vendor, product or service depicted in its publications, and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner publications consist of the opinions of Gartner’s business and technology insights organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this publication, including any warranties of merchantability or fitness for a particular purpose.
What is the Gartner® Magic Quadrant™?
“Magic Quadrant reports are a culmination of rigorous, fact-based research in specific markets, providing a wide-angle view of the relative positions of providers in markets where growth is high and provider differentiation is distinct. Providers are positioned into four quadrants: Leaders, Challengers, Visionaries and Niche Players. The research enables you to get the most from market analysis in alignment with your unique business and technology needs."
How can PAM help secure AI agents in the enterprise?
PAM can help secure AI agents by controlling their access to systems and data, protecting the secrets they use, and recording their access and actions. Capabilities vary by solution; controls should limit each agent’s permissions and how long those permissions remain active. Learn more aboutIdira Agentic Identity Security.
How does zero standing privileges differ from vaulted access?
Vaulted access protects stored privileged credentials. ZSP removes standing privileged access by granting permissions for a specific task and revoking them when the task or authorized period ends. Modern PAM can combine both approaches to support different environments and access needs.
By submitting this form, you agree to ourTerms of Useand acknowledge ourPrivacy Statement. Please look for a confirmation email from us. If you don't receive it in the next 10 minutes, please check your spam folder.
By submitting this form, you agree to ourTerms of Useand acknowledge ourPrivacy Statement.
By submitting this form, I understand my personal data will be processed in accordance withPalo Alto Networks Privacy StatementandTerms of Use.
Copyright © 2026 Palo Alto Networks. All Rights Reserved
Related articles
Barracuda Flaws Could Be Chained to Bypass Authorization and Gain Root Access
2 days ago
Google Disrupts 1.3 Million-Device Android Botnet, Says TV Box Maker Sold Criminal Access
3 days ago
Attackers Chain Three Ivanti Connect Secure Flaws to Gain Unauthenticated Root Access
5 days ago
You might Also like

Vercel rolls out new protection against stolen session cookie attacks
Zyxel fixes zero-day exploited to hack nearly 1,000 network switches

