GHSA-g3cm-qg2v-2hj5

    Dashboard / Vulnerabilities / GHSA-g3cm-qg2v-2hj5

    GHSA-g3cm-qg2v-2hj5

    Published: 5 Feb 2024Last Modified: 10 Sept 2026

    Summary: pyLoad open redirect vulnerability due to improper validation of the is_safe_url function

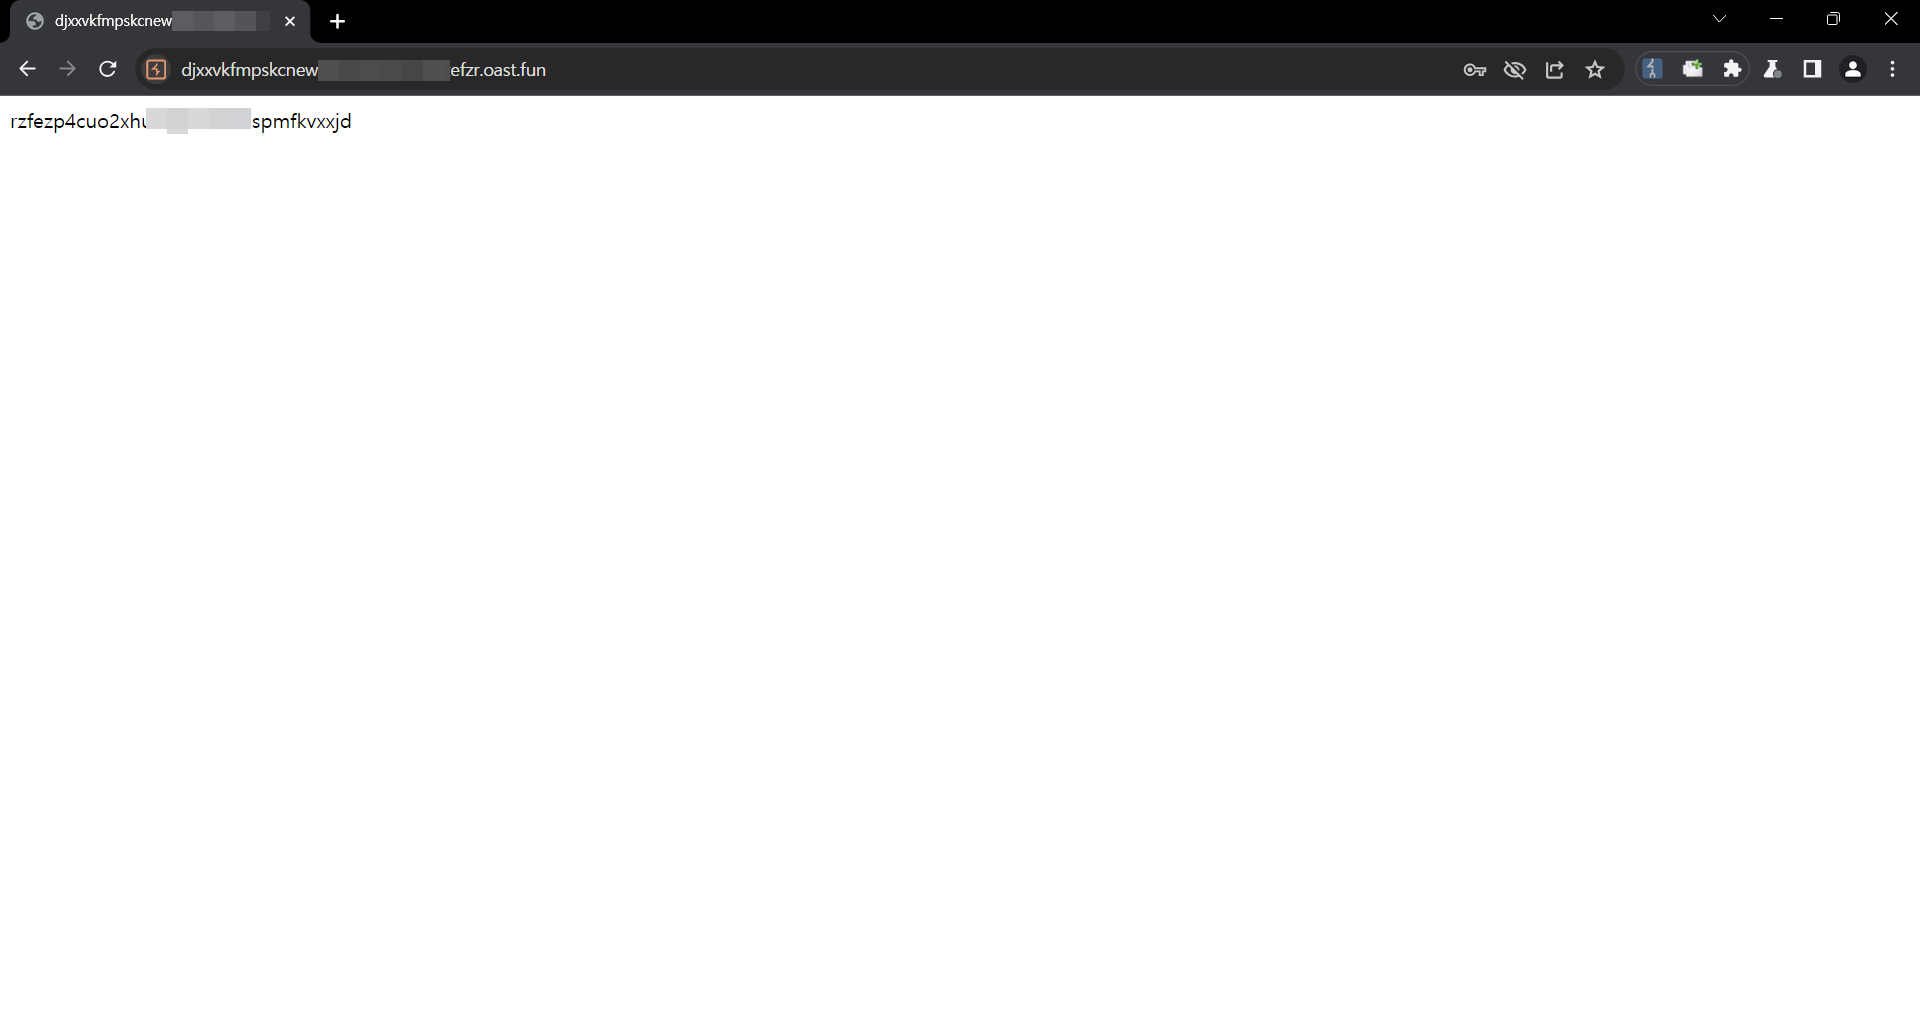
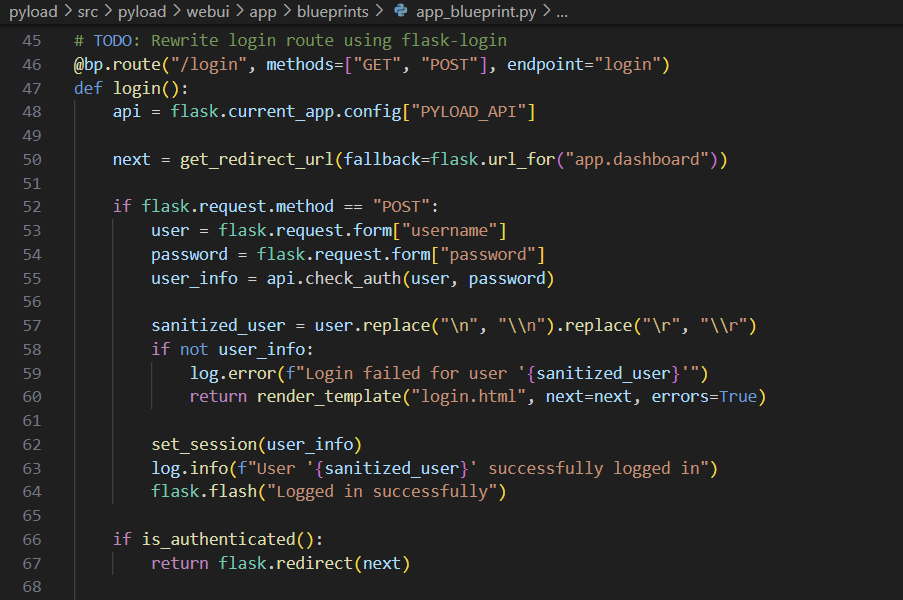
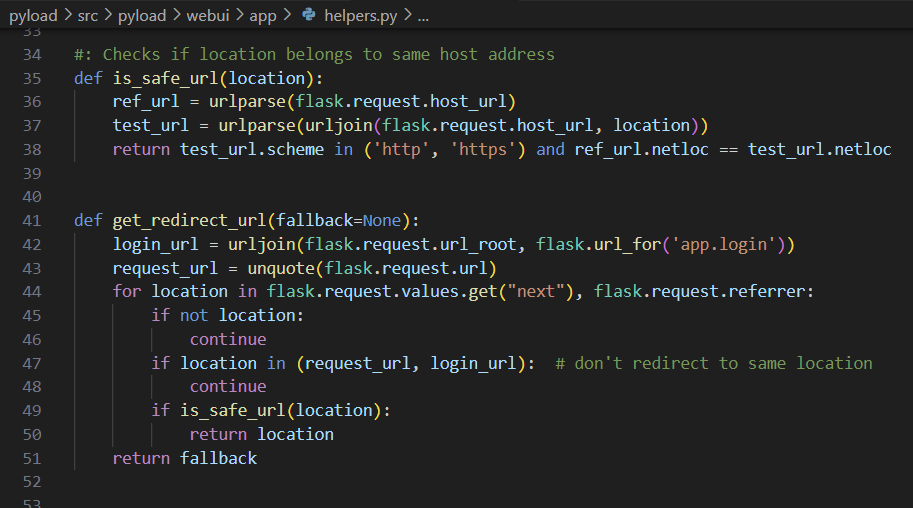
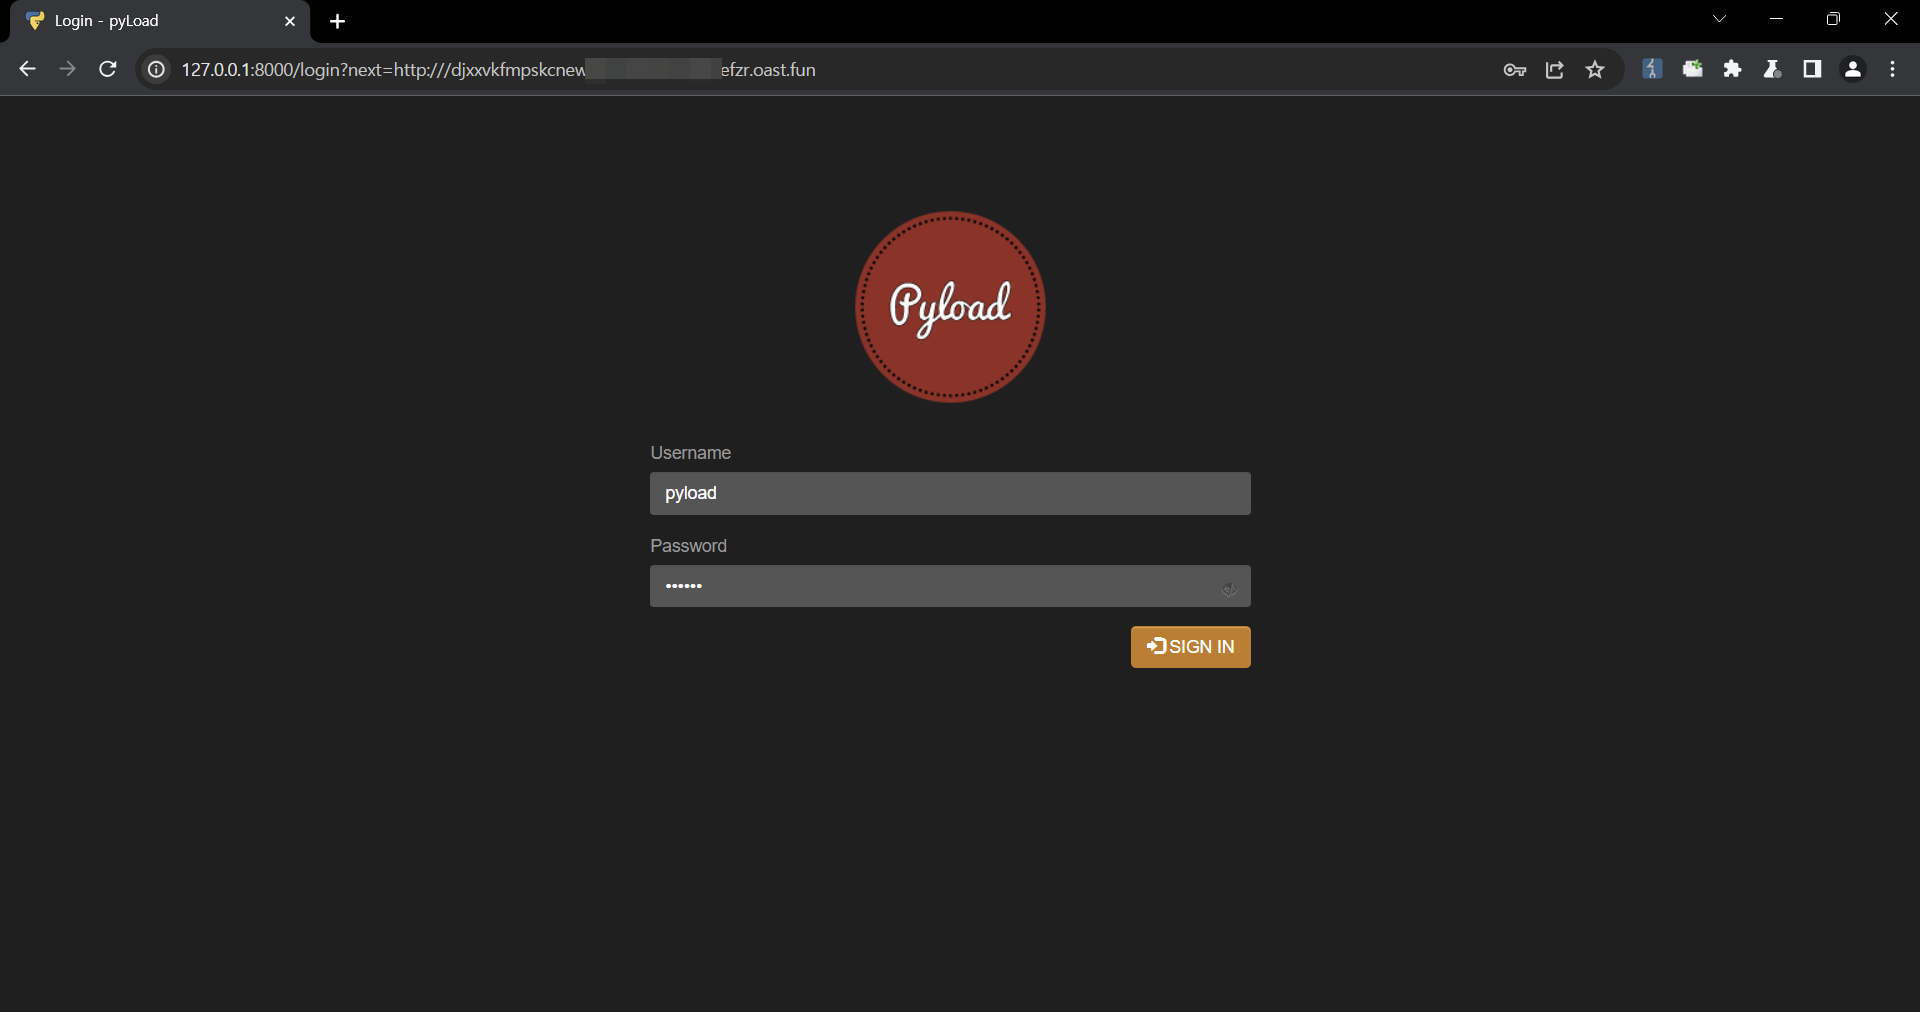
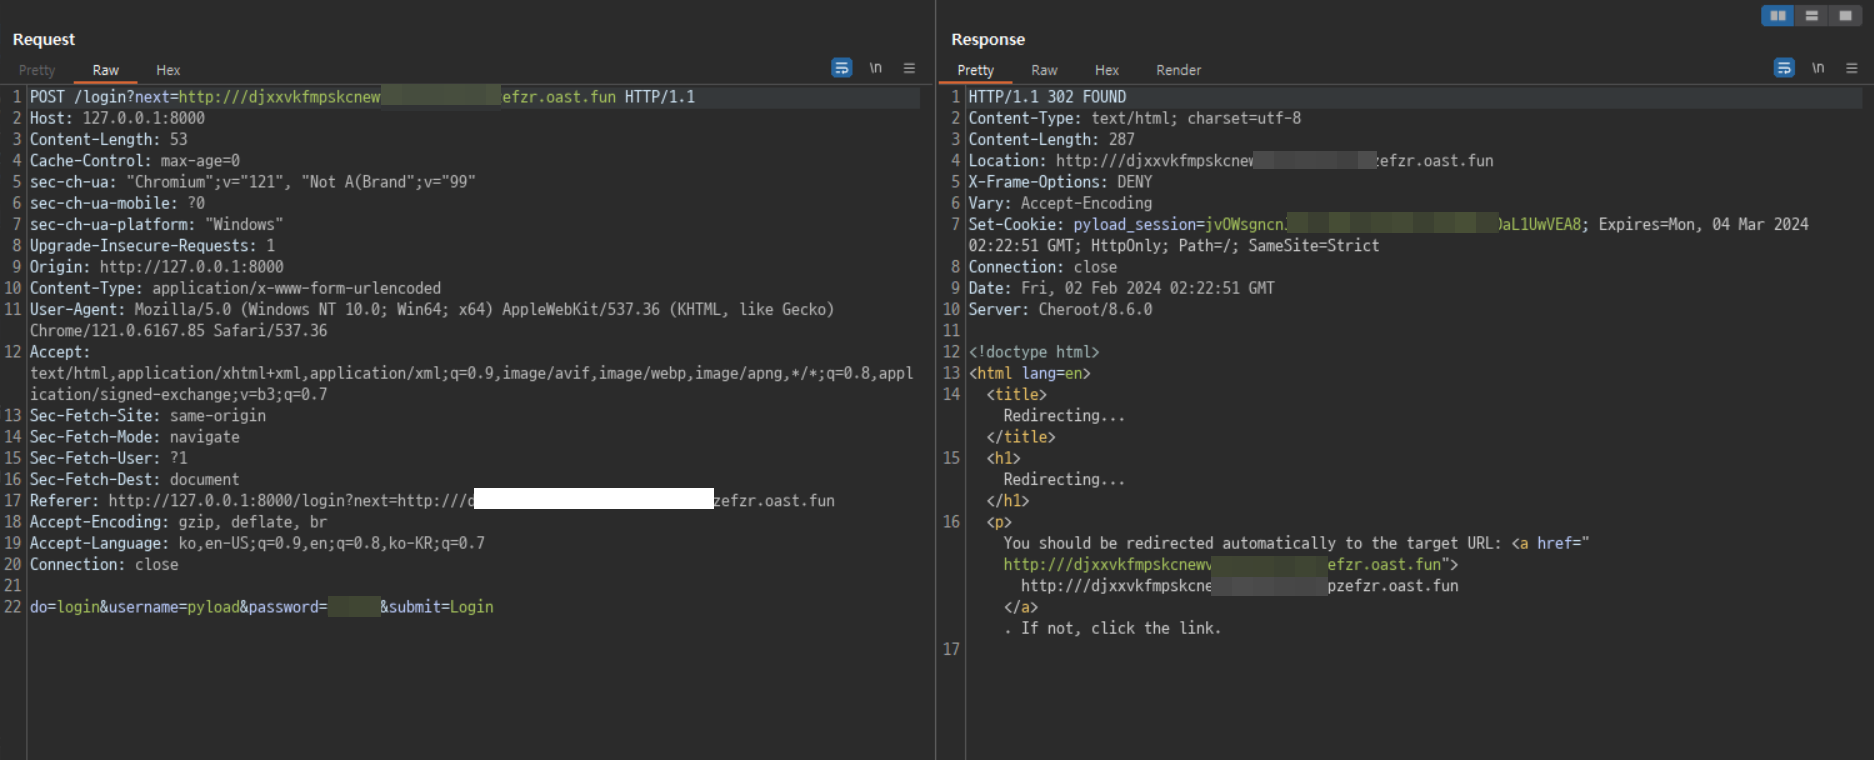
    Details: ### Summary Open redirect vulnerability due to incorrect validation of input values when redirecting users after login. ### Details pyload is validating URLs via the `get_redirect_url` function when redirecting users at login. ![301715649-f533db41-d0bd-44f7-8735-be1887fbd06c](https://github.com/pyload/pyload/assets/114328108/7fbec2ed-05ed-46e6-847f-05132cf3f136) The URL entered in the `next` variable goes through the `is_safe_url` function, where a lack of validation can redirect the user to an arbitrary domain. ![301715667-2819b1d3-8a14-42f4-89c8-3d2fa84fc309](https://github.com/pyload/pyload/assets/114328108/613484f3-8097-4871-887d-8fa5eec817cc) The documentation in the urllib library shows that improper URLs are recognized as relative paths when using the `urlparse` function. (https://docs.python.org/3/library/urllib.parse.html#urllib.parse.urlparse) For example, When an unusual URL like `https:///example.com` is entered, `urlparse` interprets it as a relative path, but in the actual request it is converted to `https://example.com` due to url normalization. ### PoC 1. In the next variable, insert the URL to which you want to redirect the user. ![301715949-bb1451eb-5e84-451d-83b4-5c3e204d1df7](https://github.com/pyload/pyload/assets/114328108/6fe639ea-1f85-4715-bf6c-c9c8c4ee9c94) 2. Check that it is possible to bypass url validation and redirect users to an arbitrary url. ![301715824-3de6584a-878d-4ec4-a3d5-a34d11c6c0ac](https://github.com/pyload/pyload/assets/114328108/902b3244-a4ef-4f8e-8319-c4b92764f15f) ![301716107-ba5ab7b9-7aa8-4b7a-8924-eba82442b4c3](https://github.com/pyload/pyload/assets/114328108/35191d7b-50b9-4a46-8319-ebdebec20b41) ### Impact An attacker can use this vulnerability to redirect users to malicious websites, which can be used for phishing and similar attacks.
    Affected packages

    Package

    Name: pyload-ng

    Purl: pkg:pypi/pyload-ng

    Affected ranges

    Type: ECOSYSTEM

    Events:

    Introduced- 0
    Fixed -0.5.0b3.dev79

    Affected versions

    0.5.0a5.dev528
    0.5.0a5.dev532
    0.5.0a5.dev535
    0.5.0a5.dev536
    0.5.0a5.dev537
    0.5.0a5.dev539
    0.5.0a5.dev540
    0.5.0a5.dev545
    0.5.0a5.dev562
    0.5.0a5.dev564
    0.5.0a5.dev565
    0.5.0a6.dev570
    0.5.0a6.dev578
    0.5.0a6.dev587
    0.5.0a7.dev596
    0.5.0a8.dev602
    0.5.0a9.dev615
    0.5.0a9.dev629
    0.5.0a9.dev632
    0.5.0a9.dev641
    0.5.0a9.dev643
    0.5.0a9.dev655
    0.5.0a9.dev806
    0.5.0b1.dev1
    0.5.0b1.dev2
    0.5.0b1.dev3
    0.5.0b1.dev4
    0.5.0b1.dev5
    0.5.0b2.dev10
    0.5.0b2.dev11
    0.5.0b2.dev12
    0.5.0b2.dev9
    0.5.0b3.dev13
    0.5.0b3.dev14
    0.5.0b3.dev17
    0.5.0b3.dev18
    0.5.0b3.dev19
    0.5.0b3.dev20
    0.5.0b3.dev21
    0.5.0b3.dev22
    0.5.0b3.dev24
    0.5.0b3.dev26
    0.5.0b3.dev27
    0.5.0b3.dev28
    0.5.0b3.dev29
    0.5.0b3.dev30
    0.5.0b3.dev31
    0.5.0b3.dev32
    0.5.0b3.dev33
    0.5.0b3.dev34
    0.5.0b3.dev35
    0.5.0b3.dev38
    0.5.0b3.dev39
    0.5.0b3.dev40
    0.5.0b3.dev41
    0.5.0b3.dev42
    0.5.0b3.dev43
    0.5.0b3.dev44
    0.5.0b3.dev45
    0.5.0b3.dev46
    0.5.0b3.dev47
    0.5.0b3.dev48
    0.5.0b3.dev49
    0.5.0b3.dev50
    0.5.0b3.dev51
    0.5.0b3.dev52
    0.5.0b3.dev53
    0.5.0b3.dev54
    0.5.0b3.dev57
    0.5.0b3.dev60
    0.5.0b3.dev62
    0.5.0b3.dev64
    0.5.0b3.dev65
    0.5.0b3.dev66
    0.5.0b3.dev67
    0.5.0b3.dev68
    0.5.0b3.dev69
    0.5.0b3.dev70
    0.5.0b3.dev71
    0.5.0b3.dev72
    0.5.0b3.dev73
    0.5.0b3.dev74
    0.5.0b3.dev75
    0.5.0b3.dev76
    0.5.0b3.dev77
    0.5.0b3.dev78

    Common Vulnerability Scoring System

    Attack Vector
    Network
    Adjacent
    Local
    Physical
    Privileges Required
    None
    Low
    High
    User Interaction
    None
    Required
    Scope
    Unchanged
    Changed
    Confidentiality
    None
    Low
    High
    Integrity
    None
    Low
    High
    Availability
    None
    Low
    High
    GHSA-g3cm-qg2v-2hj5 | CVE-DB