Cyber News
Dashboard / Cyber News

Google: LLMjacking attacks rack up $1 million in cloud AI charges

mSecure Warns Users to Change Passwords, Reset 2FA and Passkeys After Suspicious Activity
1 day ago

Chainstack Reports Production Systems Breach Exposing Customer Data and Password Hashes
1 day ago

Binance Reveals How Fake Job Interviews and AI Tool Abuse Led to $6.43 Billion Theft
2 days ago
3AM Ransomware Hits 37 UK School Systems in Suspected AI-Assisted Attack

Barracuda Flaws Could Be Chained to Bypass Authorization and Gain Root Access
2 days ago

Google Warns LLMjacking Attacks Are Costing Some Enterprises Up to $1 Million in Cloud Charges
2 days ago

cPGuard Update Channel Hijacked to Backdoor Linux Servers and Collect Password Hashes
2 days ago
Barracuda warns of critical flaws allowing root access to devices
Gartner Predicts SOCs Will Have 50% More Engineers Than Analysts by 2028
2 days ago
UK school estate hit by 3AM ransomware in suspected AI-assisted attack
2 days ago
PHP2Shell: what we know about the threat two weeks later | Kaspersky official blog
2 days ago
What to Know Before Getting a Crypto Debit Card
Cursor Distributed Claude Code Extensions With SSH Backdoor Code
2 days ago

Red Hat Patches 9.8-Rated Linux TCP RCE Flaw While Ubuntu Releases Fixes for Testing
2 days ago

The 4 Elements of Exposure Prioritization and How to Operationalize Them
2 days ago

Russia-Aligned Gorbag Hackers Exploit WinRAR Flaw to Deploy Data-Stealing Malware

Hackers Exploit BTCPay Server Flaw to Steal Bitcoin and Litecoin From Hot Wallets
2 days ago
CrowdStrike Advances AI Security and Safety from Endpoint to Cloud
2 days ago
Introducing AI Kill Switch: Taking Control When AI Agents Go Rogue
2 days ago
CrowdStrike to Acquire Dreadnode to Bring Automated AI Security Testing to the Falcon Platform
2 days ago
CrowdStrike to Acquire Fiddler to Deliver Falcon Observe for AI Agent Observability
2 days ago

Synology NAS Devices Targeted in Ransomware Attacks Exploiting Patched DSM Flaw
2 days ago

New Wave of Refrigeration Cyberattacks Hits Supermarkets Across Europe, Forcing Stores to Pull Food

Attackers Exploit Critical Siemens IoT2050 Flaw to Plant Remote Command Backdoors
2 days ago

Attackers Target Unpatched CryptoPayment Gateway Flaw That Can Expose Wallet Credentials
2 days ago
Cogent Security Makes the Fortune Cyber 60 for a Second Year, With a Plan to Run Cyber Defense Like a Factory
2 days ago
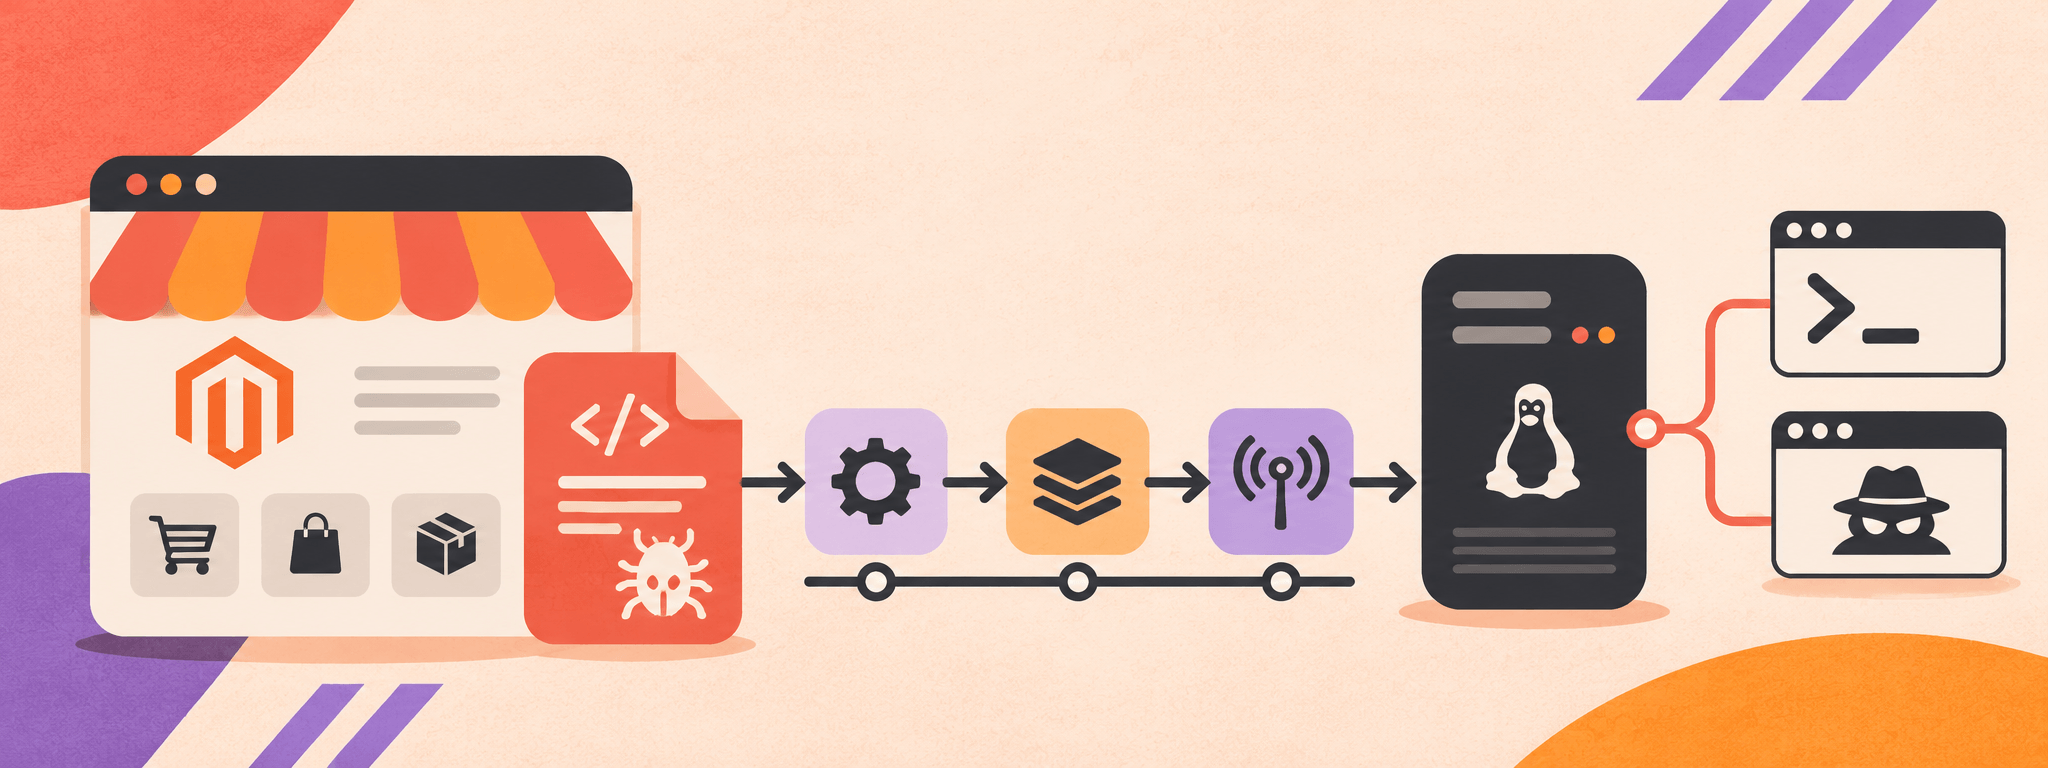
StyleSmuggler Exploitation Deploys PSK Agent RAT Against Magento Stores
TL;DR: Between September 9 and September 13, 2026, we detected a coordinated campaign exploiting Magento and Adobe Commerce stores across Western Europe, North America, and the Asia-Pacific region. The activity used /paypal/transparent/response/, an endpoint tied directly to StyleSmuggler (CVE-2026-75650). Malware recovered from the delivery infrastructure reveals a multi-stage chain that installs a shell-script dropper, a […]
The post StyleSmuggler Exploitation Deploys PSK Agent RAT Against Magento Stores appeared first on Blog.

⚡ Weekly Recap: Critical CVEs, Linux DDoS Botnet, Device-Code Phishing, Android Spyware and More

Google Disrupts 1.3 Million-Device Android Botnet, Says TV Box Maker Sold Criminal Access
3 days ago

DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment
3 days ago
Guardz Brings Palo Alto Networks Prisma Browser Protection to Small Businesses
3 days ago
How a surveillance camera can be remotely disabled: the problem and the fix | Kaspersky official blog

Critical Langflow Flaws Could Let Unauthenticated Attackers Run Code on Servers
3 days ago

Is Your SOC Ready for AI Agents? A Maturity Check Before You Deploy
3 days ago

Attackers Pose as IT Support on Microsoft Teams, Abuse AD CS to Steal Company Data
3 days ago

Government Linux Servers Targeted With SysGoRAT and Suspected AI-Generated Scripts
What Makes a Good Security Agent? 5 Lessons from the AgentWorks Hackathon
3 days ago

New VOLTA Infostealer Uses Claude, Gemini, and Kimi AI to Rank Victims by Financial Value
3 days ago

CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key
4 days ago

Hackers Steal About $2.7 Million From Polymarket Traders via Hijacked DebugBear Script

FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist
4 days ago

NetamLoader Malware Targets Government Windows 10 Systems in Asia via .NET Injection
4 days ago

Chainalysis Confirms Intrusion Into Internal Tools and Exposure of Customer Identity Data
5 days ago

Attackers Chain Three Ivanti Connect Secure Flaws to Gain Unauthenticated Root Access

Latest News
See AllCyberattack disrupts blood storage refrigeration systems in France
Critical Ruby on Rails Flaw Could Let Hackers Steal Server Secrets Through Malicious Image Uploads


