Cyber News
Dashboard / Cyber News

Cloudflare Reports 18.2 Million Network-Layer DDoS Attacks in Q3, Up 38%

Chinese Hackers Use AI-Powered ARTEX to Target Over 200 Organizations Worldwide
6 days ago

How to download and read ebooks safely | Kaspersky official blog
6 days ago

TeamViewer Flaw Lets Remote Computers Attack Users Who Connect to Control Them
6 days ago

WordPress RCE Flaw Draws Nearly 63,000 Attack Attempts in Just 24 Hours
Vulnerabilities in Request Tracker and RT for Incident Response software
6 days ago

Trezor Warns of Suspected Hardware Implant in One of Its Wallets Sold by CryptoBilis
6 days ago

Why Urgent Security Fixes Aren't Fixed. Observe, Prove, Act, Confirm Gets Them Moving
6 days ago
Vulnerabilities in Płatnik software
Vulnerabilities in ARKETEAM Protectel software
6 days ago

Syrian Hacker Behind Fake Tweet That Triggered $136 Billion Market Drop Gets 42 Months in Prison
6 days ago

Official Claude Code Extension on Cursor Marketplace Trojanized with Persistent SSH Backdoor
6 days ago

Hackers Actively Exploit Highly Critical Drupal Commerce Core Authorization Bypass Flaw

Vulnerabilities in Zimbra Collaboration software
Applying Security by Design and Cyber Immunity principles to protect AI systems | Kaspersky official blog
7 days ago
Vulnerabilities in Szafir software
7 days ago
Strengthening API and MCP Security Through Token Risk Detection with Thales Imperva API Security
7 days ago
Weak keys in eMudhra CA certificates: the risks and how to respond | Kaspersky official blog
Multiple Vulnerabilities in Apple Products Could Allow for Arbitrary Code Execution
Multiple vulnerabilities have been discovered in Apple products, the most severe of which could allow for arbitrary code execution.
- iOS is a mobile operating system for mobile devices, including the iPhone and iPod touch.
- iPadOS is the operating system for iPad devices.
- macOS is the operating system for Mac computers.
- tvOS is the operating system for Apple TV devices.
- watchOS is the operating system for Apple Watch devices.
- visionOS is the operating system for Apple Vision Pro.
- Safari is a web browser available for macOS, iOS, and iPadOS.
Successful exploitation of the most severe of these vulnerabilities could allow for arbitrary code execution in the context of the affected application or, in some cases, with root, system, or kernel privileges. Depending on the privileges associated with the application or service, an attacker could then install programs; view, change, or delete data; or take further control of the affected device.
Vulnerabilities in boneIO products
Cybersecurity in Christopher Nolan’s The Odyssey | Kaspersky official blog
10 days ago

Three Lessons Cloud Customers Have Taught Us About Multi-Cloud Security
12 days ago
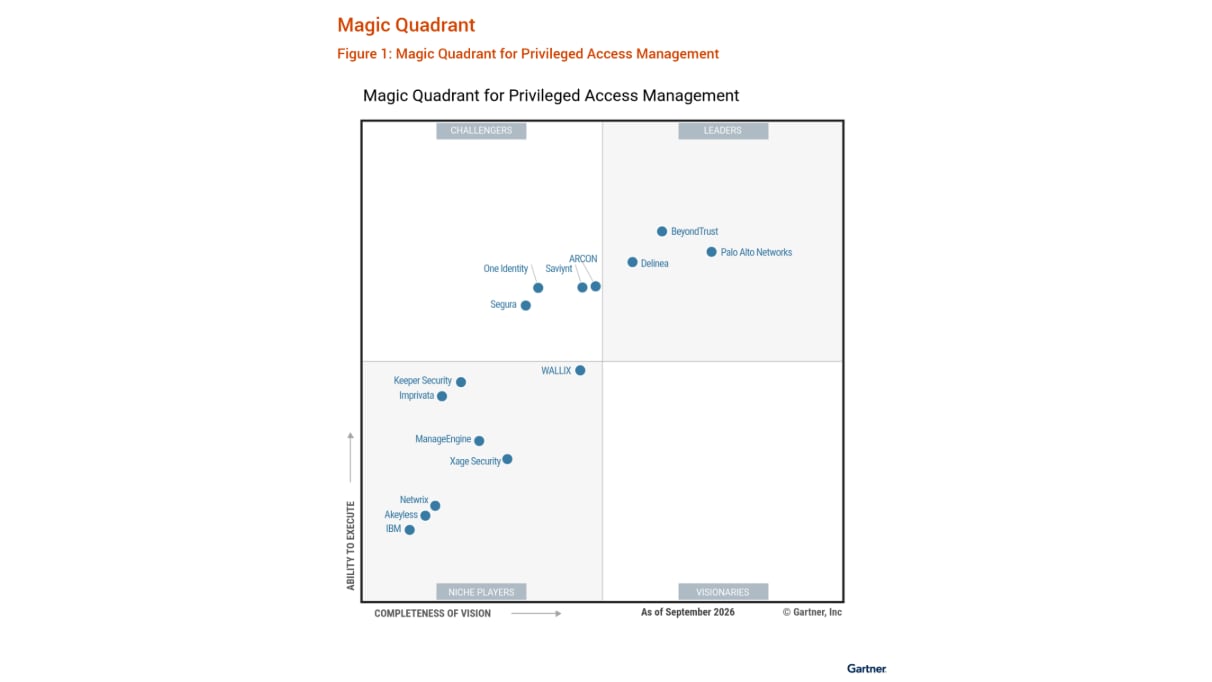
Palo Alto Networks Brings Continuous AI Defense and Prisma AIRS to the OpenAI Marketplace
13 days ago
Technology that blocks DGA domains | Kaspersky official blog
Vulnerability in MTW CleanShot X software
Millions of PHP Instances Exposed - What Organizations Need To Do Right Now
Two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) have been published. Both vulnerabilities carry a severe CVSS score of 9.2 (more technical details are in the Unit 42 Threat Brief). This is …
The post Millions of PHP Instances Exposed - What Organizations Need To Do Right Now appeared first on Palo Alto Networks Blog.
PHP2Shell: When PHP Runs Out of Memory at the Wrong Moment
15 days ago
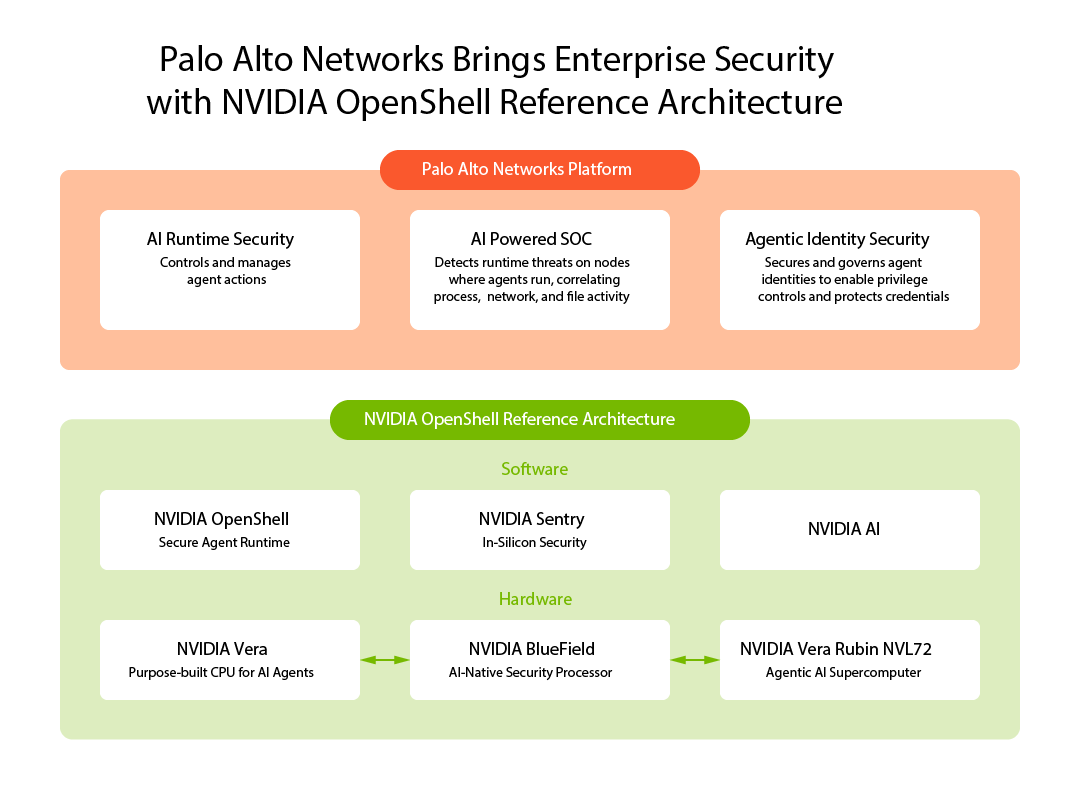
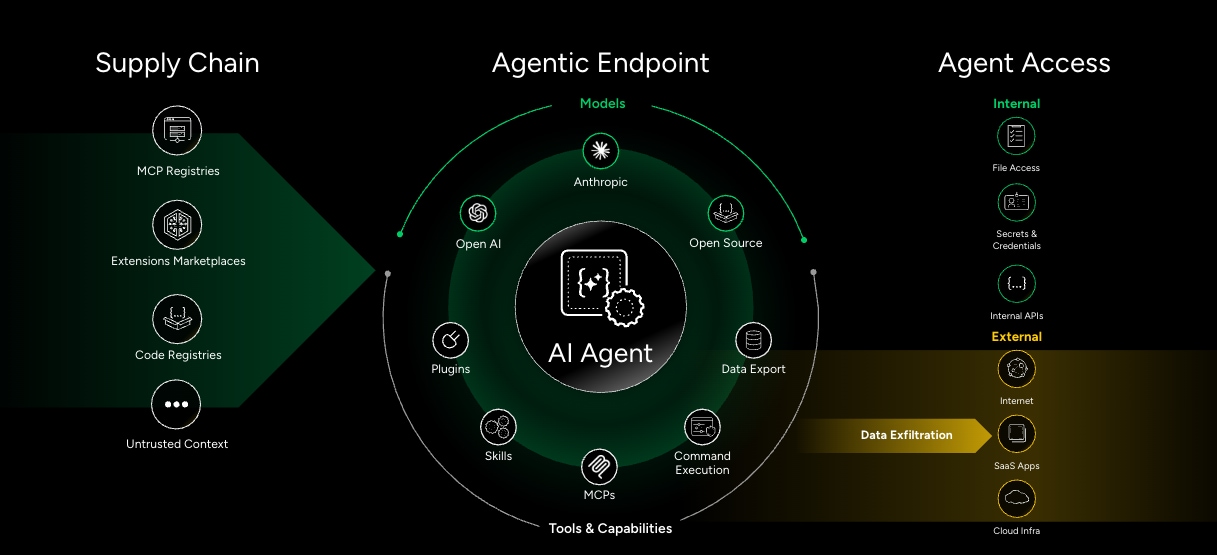
Advancing Agentic AI Security with Palo Alto Networks and NVIDIA
15 days ago
AI doxing tools: how online surveillance technology has changed | Kaspersky official blog
16 days ago
A Vulnerability in BeyondTrust Remote Support Could Allow for Arbitrary Upload of Files
A vulnerability has been discovered in BeyondTrust Remote Support that could allow for arbitrary upload of files. BeyondTrust Remote Support is an enterprise secure remote access solution that enables IT teams to securely access and troubleshoot remote endpoints. Successful exploitation of this vulnerability could allow a remote attacker to perform file operations on an affected appliance.
Vulnerability in NordVPN software
Latest News
See AllCyberattack disrupts blood storage refrigeration systems in France
Critical Ruby on Rails Flaw Could Let Hackers Steal Server Secrets Through Malicious Image Uploads


